Friday, September 4, 2015

Adobe Reader DC Update - Network Security Importance

Preface

Today, people in MOI put quite a lot of effect on updating Adobe Reader DC to the latest version. And, in this post, I would like to discuss the importance of updating software like this from security viewpoint, as well as the methods we can apply to update softwares for a bunch of computers efficiently.

Adobe Reader DC Update - Introduction

To discuss the importance of the update, we first have to find out what's new in the latest update (take 15.008.20082 planned update as example here). Then, we look into the security part (ignore the new features, bugs, etc), and take version 2015.007.20033 as affected version where we can get a list of CVE numbers.

Adobe listed out all the security issues (Common Vulnerabilities and Exposures, CVE) that affects to certain version of their Reader DC software, which look like: CVE-2014-0566, CVE-2014-8450, CVE-2015-3095, CVE-2015-4435, CVE-2015-4438, CVE-2015-4441, CVE-2015-4443, ... etc.

Each CVS indicates one security problem. For example, CVE-2014-0566 causes memory corruption vulnerabilities that could lead to code execution, CVE-2014-8450 causes security bypass vulnerabilities that could lead to information disclosure, etc. Any of these CVSs may be a huge security issue that may cause hackers to execute programs without permission.

Adobe Reader DC Update - Methods

For sure, the most basic solution is to check "Check for Updates" in Adobe Reader. However, here I would like to discuss the methods applied by IT administrators which applies updates onto multiple computers in the same time. (Although I am not familiar with Windows enough, I am discussion the things in Windows environment since that's the environment I am facing recently.)

Method 1 - AIP-GPO

AIP-GPO stands for Administrative Install Point deployed via Group Policy Objects. So, it should be divided into two parts for discussion.

AIP is a special directory created by extracting the contents of a self-contained MSI-file into a previously empty directory with the command 'msiexec /a' (applies the administrative installation option). For msp patch files, you have to run 'msiexec /p' later on to attach onto the just-applied msi file.

GPO are used to distribute settings to windows PCs that are members of a domain from a windows server. After the initial setups for GPO, you can simply select the AIP folder and apply the change. Users under a GPO policy will now get the latest update after the group policy refreshes and a computer restart.

* Without a real hands-on operation of AIP-GPO, I am not sure how does GPO find AIP folders, and how good is this solution.

Method 2 - Bootstrapper

Any setup.exe or any other executable that installs updates and launches the MSI installer is a Bootstrapper. Under Adobe's document, we can learn the following benefits of using Bootstrapper:
  • Detects whether the required Windows Installer (MSI) is available and installs it if it isn’t.
  • Detects whether the product is already installed and only proceeds if it does not exist on the target machine.
  • Provides binary installations where the entire installer is supplied and run by each machine.
  • Provides a simple way to chain updates in the required order by simply adding the msp to the installer folder and modifying Setup.ini to apply that patch.
  • It is not subject to the patch constraint that limits an AIP from installing a quarterly update over a out of cycle patch. Thus, installs can always have the latest update without starting over.
So, for our purpose, we can simply add the msp file to the installer folder and modify Setup.ini to apply the latest Adobe Reader update.

* Without having enough information, I am not sure how this solution applies to multiple machines in the same time. So far, I assume bootstrapper should be a way to install/manage updates via command line; therefore, I think, to distribute the updates onto multiple machines, we have to distribute the msp file first, then run setup.exe on each machine remotely.

Method 3 - SCUP/SCCM

"System Center Updates Publisher (SCUP) is a stand-alone tool that is used in conjunction with Microsoft’s System Center Configuration Manager (CM hereafter) to allow administrators to more accurately and efficiently install and update software. Together, CM and SCUP are Microsoft’s latest change and configuration management solution that replaces older methodologies such as SMS and GPO. Unlike those technologies, CM provides features such as metering, asset intelligence, and improved remote client administration. For example, CM users can easily determine what products versions are installed including all dot and double dot patches without having to write a complicated query." - Adobe.com

Simply to say, SCUP/SCCM is a newer solution came up after the previous two solutions. SCUP is a catelog file, CM is the way to publish/manage the updates. However, since it's a newer solution, it only works on 10.x and later Adobe products.

Summary

From the documentation and the software updates, we can learn that Adobe is caring about the security issue nicely. They publish patches to deal with known CVE problems, and offer several methods help IT administrator or individuals to update. However, without knowing the real challenge that MOI has, it's quite funny that we were doing the updates manually by visiting every user on seat.

Reference


Wednesday, September 2, 2015

Lightweight Directory Access Protocol (LDAP) & Active Directory (AD)

Preface

From a security standpoint, it's better to update your softwares all the time since the old version may have some existing security problems. There's a common name for this kind of hacking which is called "zero-day". Here's how it work: a hacker first scans the versions of softwares you are using, and if he/she found that you're using a older version software, he/she will go find if there's any existing security problem under that version. This is called zero-day since once the vulnerability is release to the public, people have zero-day to fix the problem while all the machines are under threat.

So, to reduce the threat, we keep our software updated. However, there may be tons of computers under one organization, there should be solutions under different platforms to update all the computers correctly, remotely, and efficiently.

Lightweight Directory Access Protocol (LDAP)

Short Description

"LDAP is a directory service protocol that runs on a layer above the TCP/IP stack. It provides a mechanism used to connect to, search, and modify Internet directories. It's based on a client-server model." - MSDN

Information Model (date and namespaces)

It's similar to that of the X.500 OSI directory service, but with fewer features and lower resource requirements than X.500.

API


  • initialize a session (ldap_init, ldap_sslinit)
  • bind to the server (ladp_connect)
  • modify a directory entry, etc.

Distinguished Name (DN)

A DN is a sequence of relative distinguished names (RDN) connected by commas. Typical RDNs are as below:
  • DC: domainComponent
  • CN: commonName
  • OU: organizationalUnitName
  • O: organizationName
  • STREET: streetAddress
  • L: localityName
  • ST: stateOrProvinceName
  • C: countryName
  • UID: userid
So, it looks like: CN=Jeff Smith,OU=Sales,DC=Fabrikam,DC=COM

Active Directory (AD)


"Active Directory is a directory service that Microsoft developed for Windows domain networks and is included in most Windows Server operating systems. An AD domain controller authenticates and authorizes all the users and computers in a Windows domain type network - assigning and enforcing security policies for all computers and installing or updating software. It makes use of LDAP version 2 and 3, Microsoft's version of Kerberos, and DNS" - Wikipedia

To simplify, AD is Microsoft's solution for LDAP, which is designed for Windows environment. And, yes, it's much more complicated on its domain design.

Reference


Web Application Firewall

Preface

This is the first post documenting my studies while working in Ministry of the Interior (Taiwan). Though it's my alternative military service job, I am trying my best to learn from it.

While I was in the warehouse, I found Web Application Firewall (WAF), which is a real device. And, it's my first time to see look into this device, then here's my study on it.

What is WAF?

It's a firewall that applies rules on HTTP conversation (application layer), which is defencing attacks like cross-site scripting (XSS), SQL injection, malicious sources, application layer DoS Attacks, etc.

So, what's the difference between WAF and network layer firewalls (which we use more often)? Network layer firewalls operates at TCP/IP protocol level, which only lookup rules based on IP/port. They don't care about the content in application layer.

Here's an example referring to "Guide to WAF Bypass by SecurityIdiots". The first line is a normal request, and the second is a request with SQL injection. However, the second one is detected by MOD security WAF.
http://bpc.gov.bd/contactus.php?id=4
http://bpc.gov.bd/contactus.php?id=4' UNION SELECT 1,2,3-- -

Detecting WAF

To detect WAF, we can use NMAP like:
nmap -p80 --script http-waf-detect <host> 

Does WAF Work on HTTPS?

Yes or no. Since HTTPS packages are encoded, WAF shouldn't be able to read their contents. However, there are two ways for a WAF to read SSL-protected traffic:
  • The WAF also obtains the private key used by the original SSL server.
  • The WAF runs its own SSL server which is seem and used by the client. And, the WAF would decrypt the traffic first, applies its rules, then forwards it to the original server with SSL-protected.

WAF Vendors / Players

Software (lower cost, but should avoid poor setups)
  • ModSecurity
  • AQTRONIX WebKnight
Hardware (scalability, performance)
  • FortiWeb
  • Barracuda Networks

Reference

Friday, April 24, 2015

Apache Configuration

Preface


Writing Apache config file is required and basic for setting up a new website using Apache. It's easy for basic types of websites since you can find template files online, and only a little modification is needed. However, this turned out that I still don't really know much about how to write the config file even I have set up tons of websites already.

Setting up simple static websites with virtual host, or setting up Wordpress websites is easy. But, if we want to fully and nicely control the permission or setup a Django app would be complex. So, I am writing this article as a note about Apache config files.

Environment

I am using Ubuntu 14.04, so I installed those tools by having following commands:

Then, instead of modifying existing config files, I think it's a better idea to add new files under /etc/apache2/sites-available to extends the setting. For my case, I add "bugkiller.conf" for my new website called Bug Killer.

Also, since in most of the time, I build more than one website on a machine, so "virtual host" became essential setting in my case. This is the way to make Apache gave different outputs based on its domain name.

Case 1. Setup Static Websites (using Virtual Host)

  • ServerAdmin is the email address where receives error logs (or any other logs based on your setting),
  • ServerName and ServerAlias are the domain name for your new website,
  • DocumentRoot is the root directory path of your static website folder
  • For logging, it means that logs at LogLevel "warn", and will be saved in ErrorLog and CustomLog.
And, in order to let the web server process to access the folder correctly, we give the folder all the permission by saying "AllowOverride All".

Case 2. Setup Wordpress Websites (using Virtual Host)

Same as "Case 1".

Case 3. Setup Django Applications (using Virtual Host)


  • WSGIPythonPath: The path for Django project root folder. By setting up this correctly, the server process will know where are those python files locate.
  • WSGIScriptAlias: The path to Django wsgi file, which is a gateway that wires external sockets to our Django project. So, Django should start to work after setting up this path correctly.
  • Directory tag: This part is pretty alike static files, one should give out the permission to read wsgi.py file in order to access the gateway.
  • For static files, Apache server has to handle the since it is not supported when DEBUG=FALSE in Django setting. What we have to do is route the "/static/" requests to our static folder and give out permission for that folder.
  • LogLevel debug: This helped me a lot for debugging, which allowed me to read the setting errors in the default log file (/var/log/apache2/error.log or /var/log/apache2/access.log)

Friday, March 27, 2015

A Fast Way to Generate LaTeX Document using VIM

Finally, I found a fast way to generate a LaTeX document using VIM, which allows me have a basic LaTeX document within few seconds. However, a little background knowledge on MarkDown syntax is required (MarkDown Cheatsheet is here).

Step 0: setup

a. install pandoc

b. add one line of setting into .vimrc (only have to do once)

map \md <ESC>:!pandoc -V geometry:margin=1in % -s -o %<.pdf<CR>:!open %<.pdf<CR>
This is for Mac, if you are using other system, please change "open" to any PDF reader you have on your machine.

Step 1: open a new .md file

vim test.md

Step 2: write some MarkDown and save

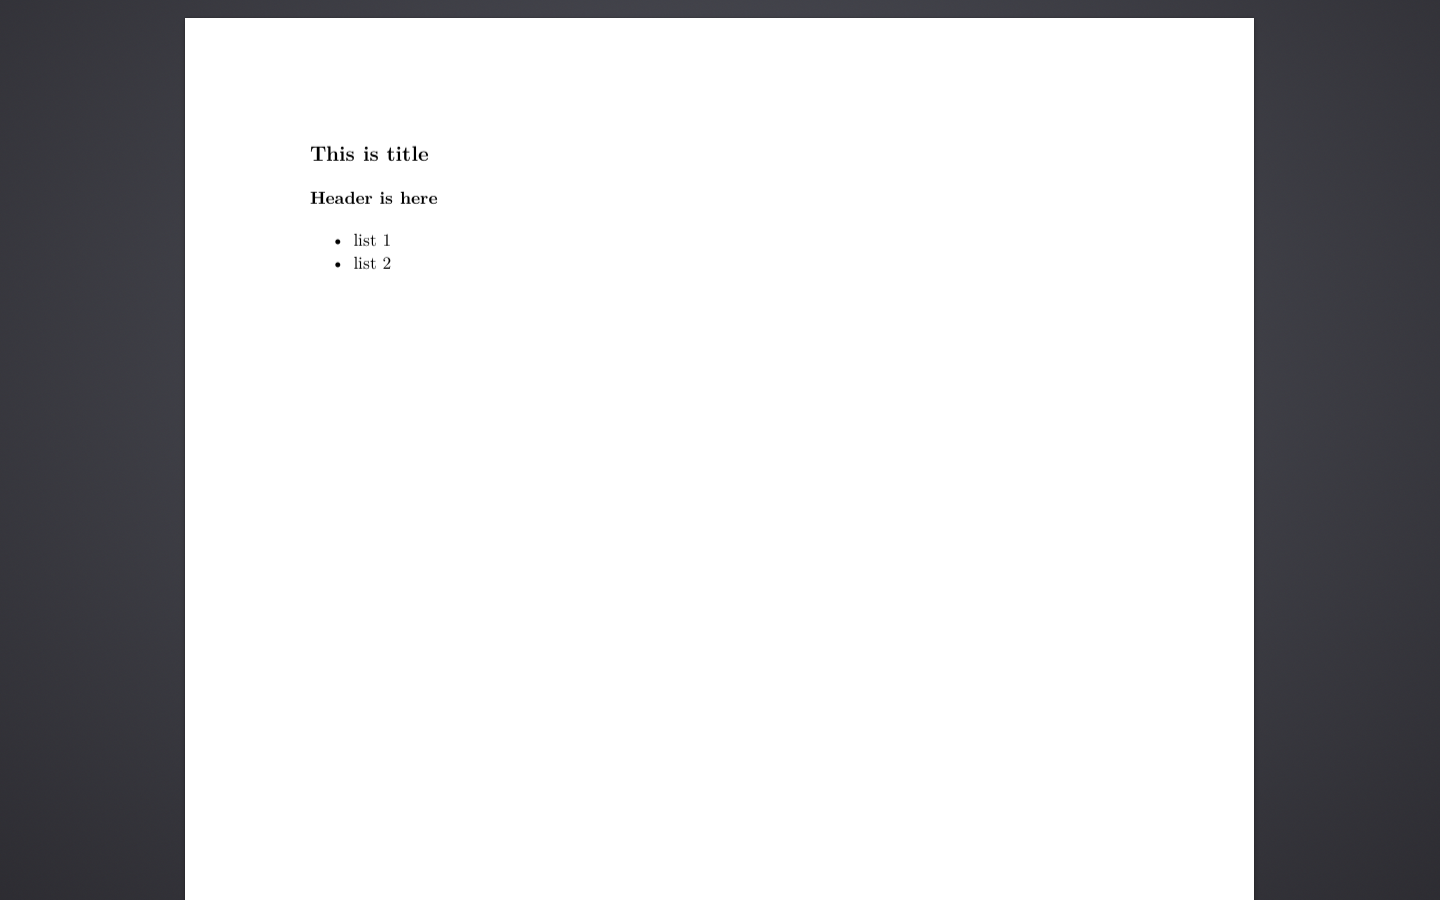
## This is title

### Header is here

- list 1

- list 2

Step 3: press following keys in vim: <ESC> \ m d


PDF file will popup automatically

Notice

  • More settings can be passed into pandoc by adding parameters.
  • This is fast way to have basic LaTeX documents, but may not be the most customised way.

Friday, March 20, 2015

Setup Semantic UI

Preface

There are tons of front-end development frameworks, and Semantic UI is one of them. I found it's support more elements than other with complete design. So, I am trying out this time.

Dependencies

There are the things needed to be install before get started:
  • node
  • gulp
    • npm install -g gulp
Other dependencies for Semantic UI:
  • cd <Semantic-UI directory>
  • npm install

Build Framework

So, we can customize our design or change the theme on Semantic UI (not included in this post), then it will generate some CSS and JS files for our website to use.
To generate the files, type: "gulp install"

Reference

Thursday, March 19, 2015

SASS - Helloworld

For people who write CSS may know that it's kind of annoying, SASS and SCSS became the solutions. We've learned some basic SCSS code in Advanced Web Design class today, and it's here.

To compile the SCSS, run "sass --watch ." in the background, and it will update the CSS file constantly.

And, I also asked Prof. Twigg which one should I go with as a beginner, SASS or SCSS. He said SCSS, which is newer.